Bug Bounty1.
Look closer. Find the flaw. Explain the impact.
Explore web vulnerability classes, investigation with Burp Suite, reconnaissance, and reporting. Build a method for examining application behavior within an explicitly authorized scope.
Open the courseLogin and course access required for lessons.

A request. A response.
A closer look.
/lab/projectThe account owns this project.
Interactive illustration · no real requests or scans.
A finding starts
with a better question.
For learners interested in web application security and responsible vulnerability research.
Observe
Know what the application is meant to do.
Investigate
Compare the expected behavior with what you see.
Communicate
Explain the observation and its impact clearly.
Follow the request. Question the behavior.
Choose a step to explore.
Understand the application
Begin with application behavior and a clearly authorized scope. Observe what is supposed to happen before looking for unexpected behavior.
Illustrative example · explore these concepts in the course.
1Training application2 → Understand the user journey3 → Observe requests and responses4 → Confirm the testing scopeFrom first observation to a clear report.
Explore the course topics before opening your lessons.
Chapter 1Introduction
Start with the Bug Bounty 1 introduction.
Chapter 2Fundamentals
Build context with the two fundamentals lessons.
Chapter 3Burp Suite
Follow the installation and tool explanation lessons.
Chapter 4IDOR
Explore insecure direct object references and access-control concepts.
Chapter 5XSS
Study cross-site scripting through the existing XSS lessons.
Chapter 6Race Condition
Explore how timing and concurrent actions can affect application behavior.
Chapter 7Information Disclosure
Study unintended exposure of information.
Chapter 8Business Logic
Explore application rules and unexpected workflows.
Chapter 9Host-Header and Response-Manipulation
Study host-header and response-manipulation concepts.
Chapter 10CSRF
Explore cross-site request forgery through the existing lesson.
Chapter 11Recon
Work through the reconnaissance chapter.
Chapter 12Reporting
Learn to communicate your findings responsibly.
An understanding of web fundamentals and introductory cybersecurity is recommended.
What stays with you?
Explore what each part of the course helps you understand.
Learn from research
beyond the classroom.
Real findings. Responsible disclosure. Experience that informs the teaching.
Oussama Barbar
Foxvoid Academy founder & cybersecurity instructor
Oussama has identified and responsibly disclosed web vulnerabilities affecting organizations including Yahoo, TeamViewer, and Withings, through platforms such as HackerOne and YesWeHack.
- Yahoo
- TeamViewer
- Withings
Recognized by Apple
He also identified and responsibly reported an iOS vulnerability, receiving recognition on Apple’s Security acknowledgements page following the release of iOS 27.
Apple Security acknowledgements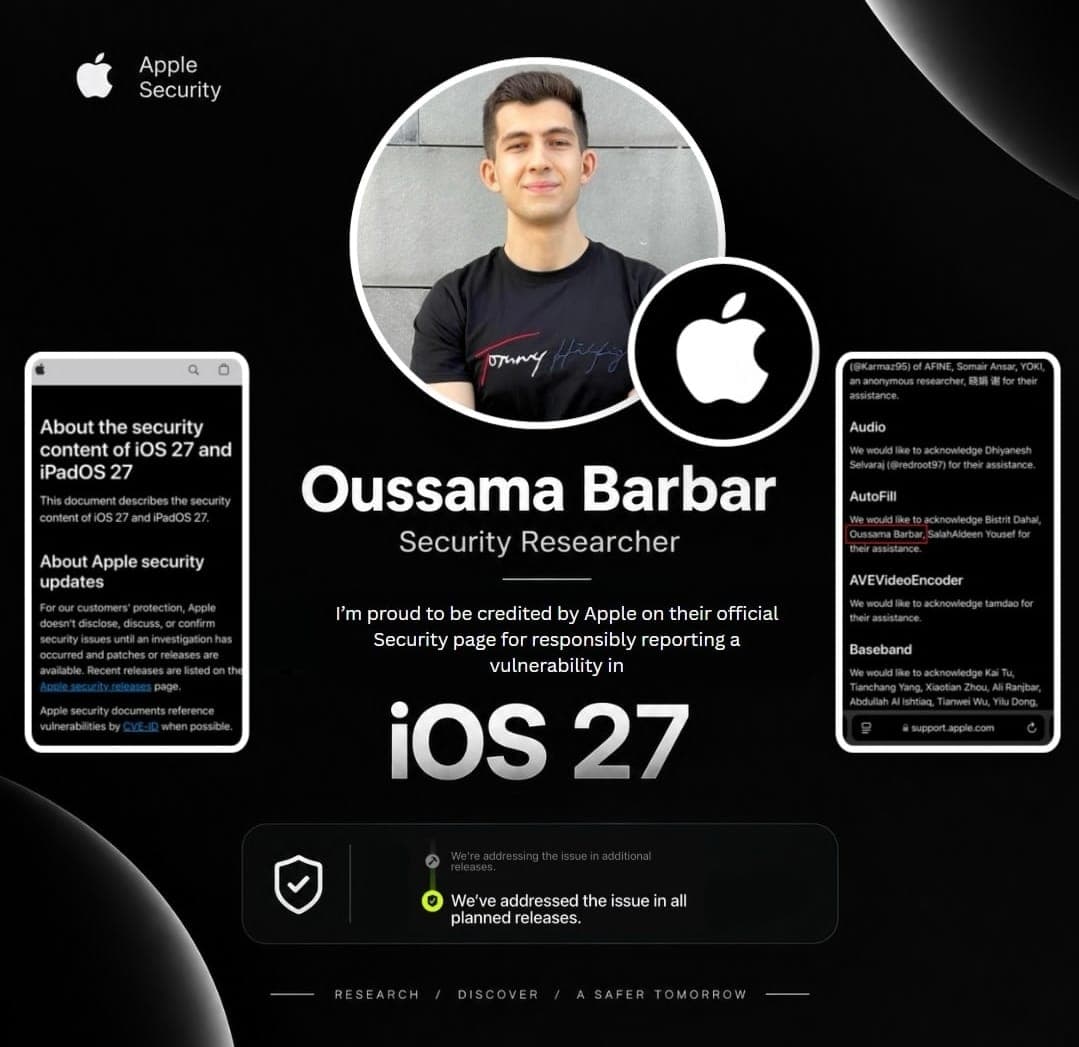
A few things
before you begin.
What should I know first?
An understanding of web fundamentals and introductory cybersecurity is recommended.
What does this course cover?
Explore web vulnerability classes, investigation with Burp Suite, reconnaissance, and reporting. Build a method for examining application behavior within an explicitly authorized scope.
How do I access the lessons?
Open the course and log in with your Foxvoid account. Your account needs access to Bug Bounty 1 to view its content.
Are these live tools?
The interactive examples on this page are illustrations. The course lessons remain in the learning portal. Practice security techniques only within an explicitly authorized scope.